Is your email signature compliant with the General Data Protection Regulation (GDPR) standards?
Not sure? Don't worry, we're here to help!
Here is our practical guide to learn more about the compliance of your email signature—and more broadly, your emails—with GDPR.
Personal data has been defined by the National Commission on Informatics and Liberty (CNIL) as "any information relating to an identified or identifiable natural person." In this sense, a simple name, photo, postal address, phone number, or a variety of other information can be considered personal data.
Note that according to CNIL's definition, personal data can be both direct and indirect:
In both cases, the management of this personal data must comply with the applicable regulations.
Yes! Since an email signature can contain personal information such as name, surname, phone number, email address, or even a photo, it is indeed considered personal data.
As a company, you must ensure that the processing of your employees' personal data through their email signatures complies with the obligations of the GDPR (as described by CNIL).
Respecting these obligations is crucial, as non-compliance could lead to a fine of up to 4% of the company's annual global revenue.
The "signature object" itself is not directly subject to GDPR, but its content is. If you've chosen to include personal data of your employees (name, phone number, etc.) in corporate signatures, you indeed have certain obligations.
To comply with the regulation, the employer must inform employees that their personal data will be used for the creation of their email signature. Employees should also be made aware of their rights (access, correction, deletion, etc.) regarding this personal data.
If you're using a tool to manage your email signatures, be aware that the personal data that passes through your email signature tool must also comply with GDPR.
For example, at Letsignit, we follow the highest protection standards for information security. Our solution is certified under ISO 27001 and ISO 27018, ensuring our clients the confidentiality of their data, with encryption and full traceability of our actions.
Be careful! Not all solutions will protect your data this way! We encourage you to reach out to the data processing officer of the solution you choose to learn more.
What about email campaigns? How do you ensure you're complying with legal obligations when sending emails?
The recommended approach will vary depending on your recipients.
You must obtain prior consent from individuals on your mailing list. This is also known as "opt-in," a mechanism that prevents people from receiving communications without having agreed to them in advance:
Even after agreeing to "opt-in," any person has the right to change their mind and choose to stop receiving commercial communications. This is known as "opt-out." You must ensure that, through your data processing officer, such a mechanism is in place.
The only exception to the "opt-in" process is when personal data (email address) is collected during a commercial transaction, and it allows the company to send advertisements for similar products. In this case, prior consent is not necessary, but the consumer must still have the option to unsubscribe and stop receiving such communications.
Email marketing to businesses, unlike emails to consumers, does not require an "opt-in" process. However, that doesn't mean businesses don't have rights—communicating with a business in this way gives the company the right to opt-out. The company can therefore choose to exit the mailing chain via an "opt-out," which must legally be respected.
For more information, please refer to the GDPR Guide from the Ministry of the Economy and Finance.
Currently, in France, it is not required to state how you process personal data in each of your emails. However, some companies still choose to include certain legal disclaimers in the form of a disclaimer.
Including such a notice in your email signature can enhance transparency and trust with your correspondents while emphasizing your commitment to data protection. This practice also promotes compliance and educates your contacts about your privacy policies, which can be a valuable asset in your professional communications.
For example, you might include "This email complies with GDPR" in your email signature to reassure recipients:
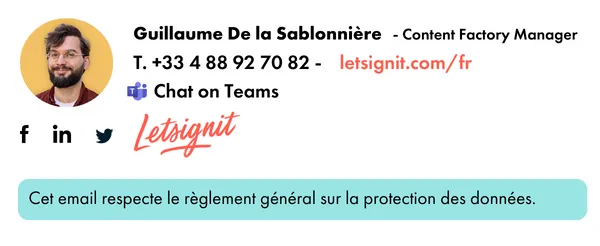
If you work in a field where confidentiality is important (e.g., healthcare, legal, consulting), the signature can also serve to remind others that the information shared is confidential:

If you use the email signature to highlight your compliance with GDPR or commitment to data confidentiality, you'll need to ensure that it adheres to a certain format.
Why is the format of your email signature important?
Because if it doesn't display well on different devices, is difficult to read, or appears pixelated, your message may not be properly conveyed. And if it can't be read correctly, what's the point of including it in the first place?
For optimal reading, we recommend:
Also, ensure that in terms of design (presence of iconographic elements, color choices, etc.), the signature is not too cluttered and, therefore, hard to read.
At Letsignit, we work hard to provide a tool that respects GDPR. Thanks to this commitment, many clients can create professional email signatures without compromising their personal data.
And in the same spirit, we pledge never to use our clients' personal data for anything other than creating email signatures.
Ready to try the simplest and most secure email signature solution on the market?